3 Weird Things in My Honeypot Logs
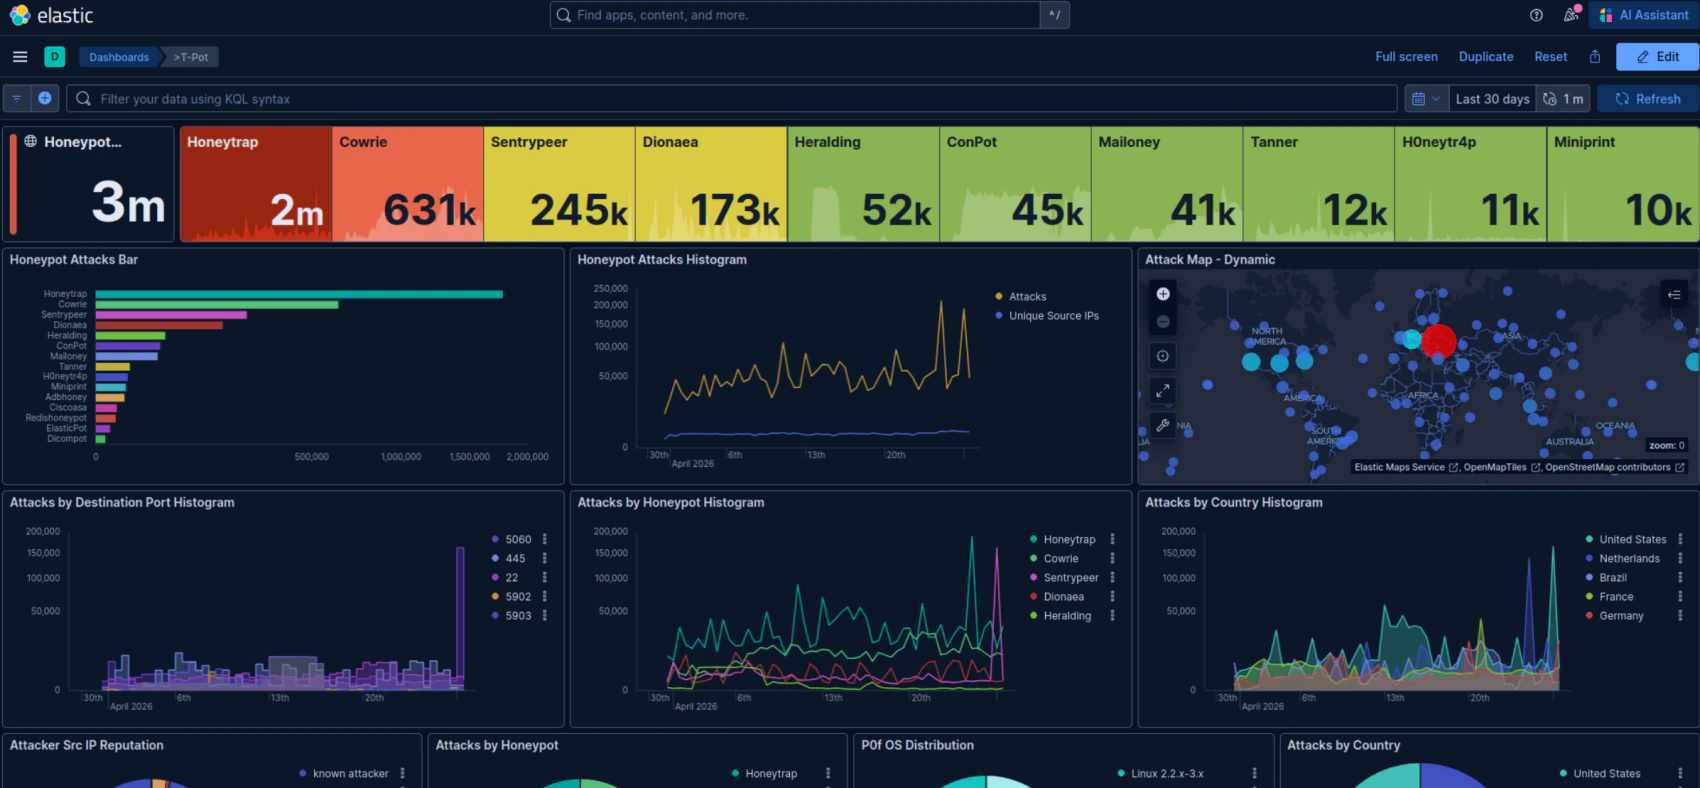
I ran a honeypot in Ukraine for a month. It received 3 million (mostly) malicious requests. Many of the bots that 'got in' (into the honeypot's fake shell) dropped a payload, and that's what I spent my time looking at.
Here are the three weirdest things I found.
3. Deep Sorrow
I started with a simple Mirai-style (DDoS bot) binary.
I ran strings on the binary to pull out all readable text, and found something unexpected.
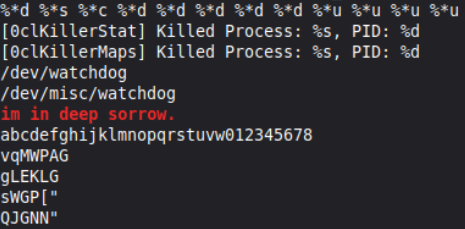
I hope they are doing fine.
Hash: c8e8f6236e6bbcee6c407cdd425432e1819871ce5231a1511a0f6ae29ac4cb68
2. Xinchao
A Mimikatz (Windows password stealer) payload came as a large password-protected ZIP.
Attackers use encrypted ZIPs so antivirus scanners can't look inside.
The password, though, was quite trivial, xinchao123, "hello123" in Vietnamese.
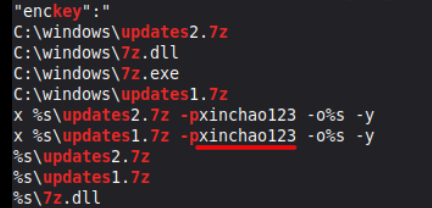
A binary was dropped alongside the ZIP file. It scans the local network for vulnerable Windows servers and deploys the Mimikatz payload to them. Inside that binary was the extraction command with the plain-text password, like in the image above.
Hash: 232bee8de476e68cb04df514bf349a5c4fa6507997f0a215804b44a81997a03b
1. YouTube
Another Mirai-style binary turned up a famous YouTube link. I know the link by heart. Do you?
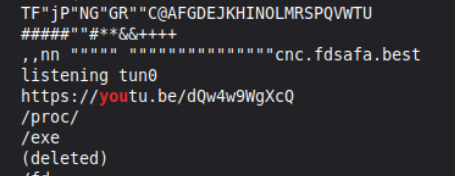
Check it out: https://youtu.be/dQw4w9WgXcQ
Hash: 32082aa7083c24581bdfe9411788040a9eed3b03ff55201f42c808c74cf24ea1
Consider running a T-Pot yourself (github.com/telekom-security/tpotce). Thanks for reading :)